Application security controls
Hotel-scoped access, call authentication, payment verification and the technical boundaries of external connections.
Content reviewed:
Security foundation
Incoming calls are verified at the source, linked to the correct hotel by phone number and deduplicated. User access is restricted by hotel membership, role and action permission.
Hotel and user boundaries
Hotel membership, operation permissions and database row access rules work together. Two-factor authentication is mandatory for platform administrators and can be enabled by hotel users. Reservations, finance, integrations and assistant settings use separate permissions. Correct production configuration remains necessary.
Call and transaction verification
Vapi events are authenticated with an account-specific secret; the hotel comes from an active phone mapping rather than a guest-supplied tenant ID. Native reservation access and cancellation check the stored phone, calling number and booking code. Repeated events use operation keys.
External PMS safety boundary
When an external system owns inventory, an outage does not enable sales from local snapshots. A second authoritative PMS and switching with pending native payments are blocked. Live offers validate property, call, stay, expiry and booking origin. These controls require the relevant database migrations.
Secrets and outbound connections
Integration credentials are encrypted with AES-256-GCM and the decryption key stays in the server environment. Custom adapter requests use HTTPS, allowed destinations, signatures, size limits and deadlines. This does not mean every database, backup or provider store uses the same encryption scheme.
Payments and audit trail
Card data is entered on the payment provider’s page. Payment signatures and amounts are validated before a booking is treated as paid. Important administration actions are audited and remain subject to access and retention policies. The notification queue supports retries and failure review.
Operational and verification limits
Backups, restore tests, access reviews, domains/TLS, monitoring and provider permissions belong in the operating plan. A control in source code is not by itself proof that it runs in production. This document does not present ISO 27001, SOC 2 or PCI DSS certification, or an independent penetration-test report.
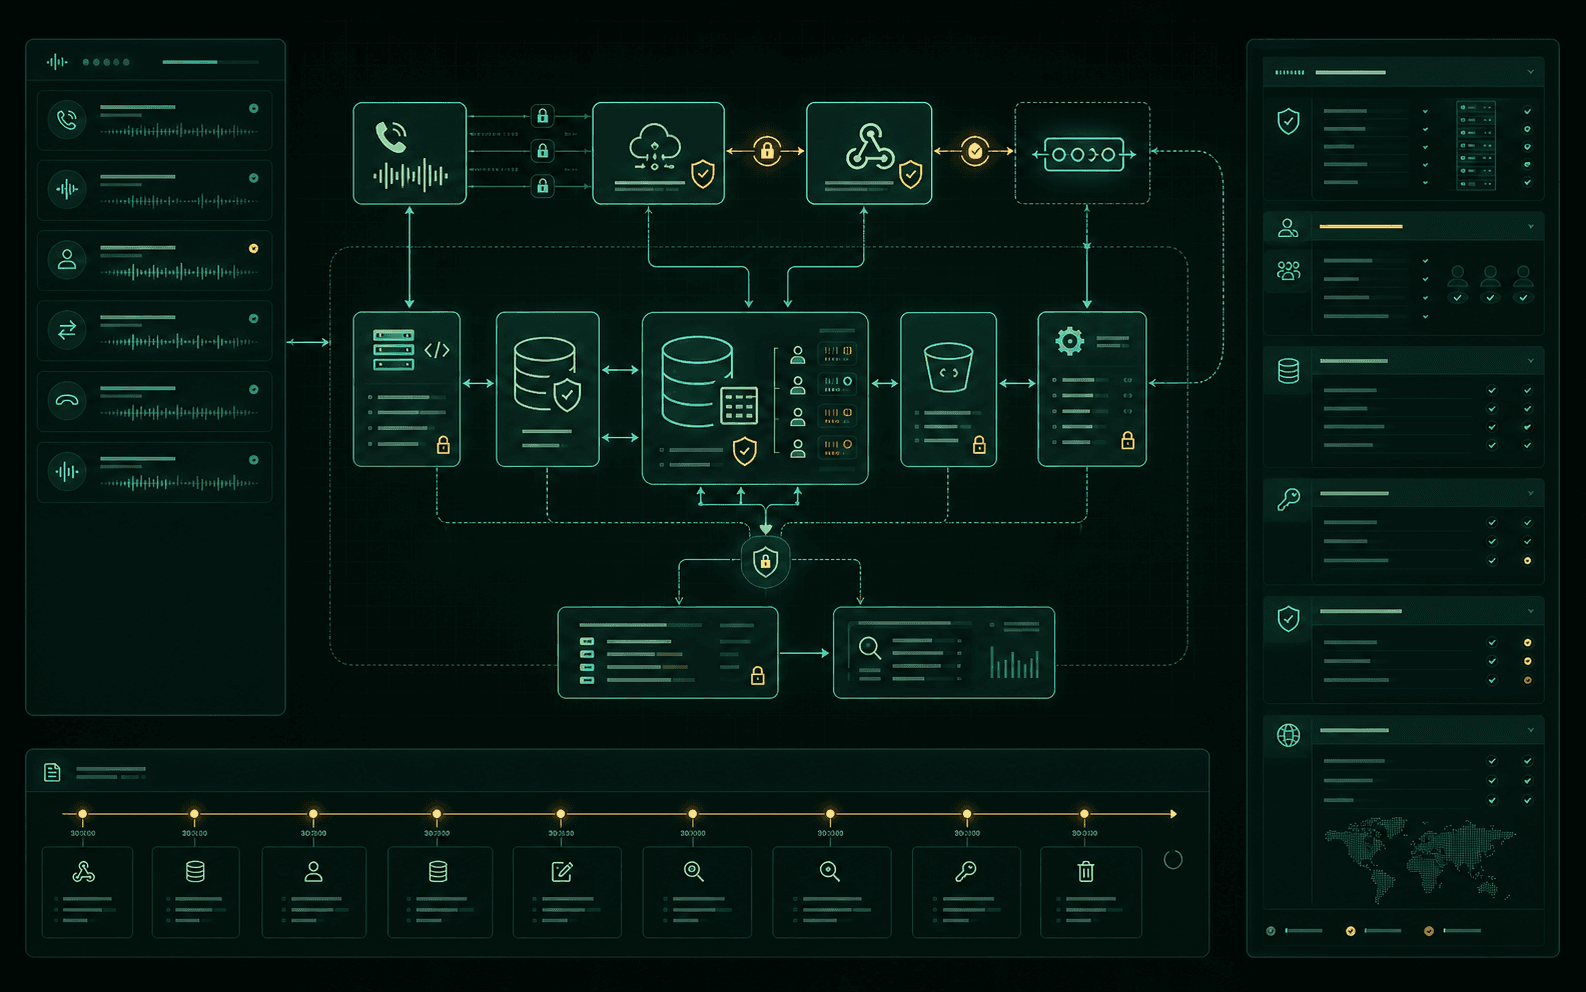
Security control points
Call event processing
Auditable workflowThe security whitepaper reflects the product design
This architecture supports security claims with auditable product behavior.