KVKK and the data processing framework
Application and operating responsibilities for notices, recording choices, individual rights, retention and cross-border transfers.
Content reviewed:
Compliance operations
The hotel's disclosure can be read at the start of a call. Recording, explicit consent and other legal bases must be determined by the hotel and its counsel for the specific scenario; the platform does not replace that assessment.
Separating notice and consent
A notice should explain the controller’s identity, purposes, recipients, collection method, legal basis and rights. Activities requiring explicit consent need a separate choice. Accepting a privacy policy, using the service or staying on a call is not automatically valid consent for every processing activity.
Official KVKK sourceRecording and real-time speech processing
Setup offers audio recording, transcript-only or disabled storage preferences. The spoken notice and technical recording setting must be reviewed together. Disabling storage does not stop real-time speech processing needed to respond. Any non-recorded alternative and staff transfer should be tested in the hotel’s actual call flow.
Official KVKK sourceLegal basis and purpose limitation
Accommodation enquiries, security logs, accounting, conversation quality and marketing have different purposes. Each activity needs an appropriate legal basis, scope and retention period. Providing contact details for a booking is not advertising permission. Free-text fields should not request sensitive data or unnecessary identity documents.
Cross-border transfer assessment
Identify actual recipients and countries for voice, model, messaging, hosting and support services. Select an applicable transfer mechanism and safeguards under KVKK Article 9 for the actual data flow. HTTPS or hosting the application in Türkiye does not by itself establish lawful transfers to other providers.
Official KVKK sourceVisitor measurement choices
Optional analytics is disabled on first visit. Visitors can accept, reject or change their choice later. Rejection removes analytics identifiers and campaign data from the browser; essential session cookies operate separately. Do Not Track and Global Privacy Control signals also disable measurement.
Official KVKK sourceRetention and request handling
Document separate retention periods for audio, transcripts, summaries, logs, reservations and financial documents. Deletion requests must consider the application, external providers and backups, including legally retained records. Automated maintenance does not replace the duty to assess an individual’s request.
Before going live
The hotel and service operator must complete their controller roles, notices, request contacts, contracts, recording choices, transfer basis and retention plan. Technical features support legal assessment; they do not establish automatic KVKK/GDPR compliance or certification for every hotel.
Compliance records
Audit sequence
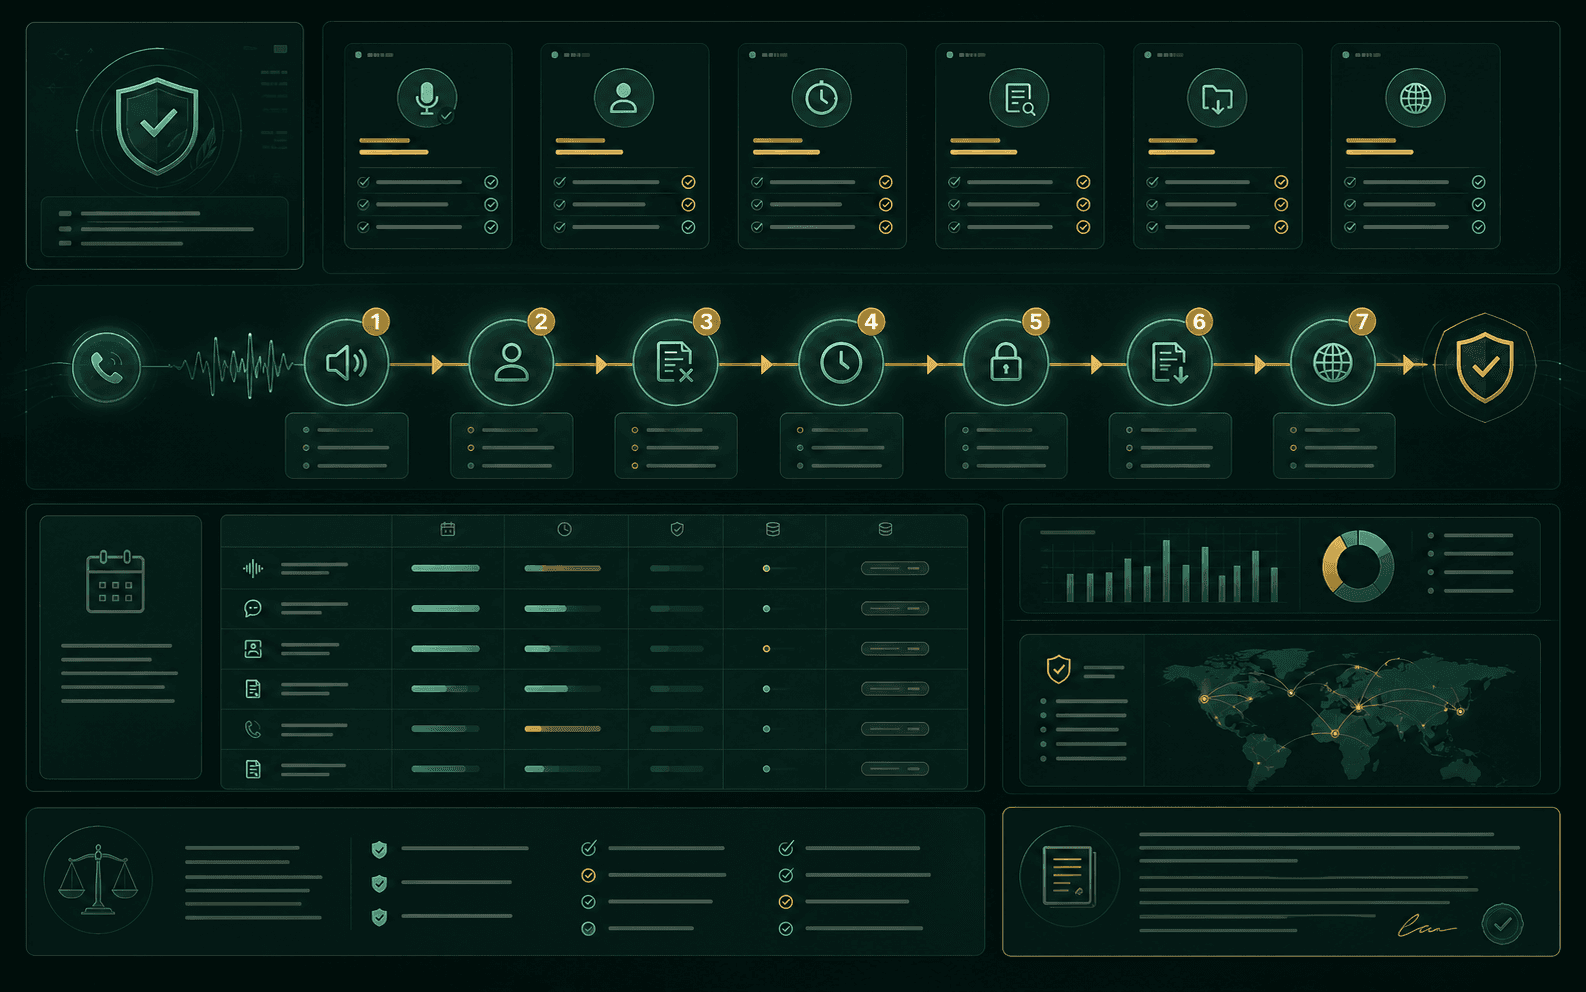
Auditable workflowCompliance is more than page copy
This framework explains technical controls; final KVKK obligations, controller responsibilities and legal notices must be assessed separately for the hotel's specific use.